
Chairperson Cho Hyun-sook: "Security cannot be an afterthought... It must be internalized from the AI design stage"
Cho Hyun-sook, Chairperson of the CODEGATE Security Forum, emphasizes that security must be integrated into the initial design phase of AI systems rather than…
As artificial intelligence (AI) technology advances rapidly and the utility of AI agents increases, points have been raised that a fundamental change in the security paradigm is necessary. The analysis suggests that the method of adding security solutions to existing systems can actually hinder system efficiency and increase security vulnerabilities.
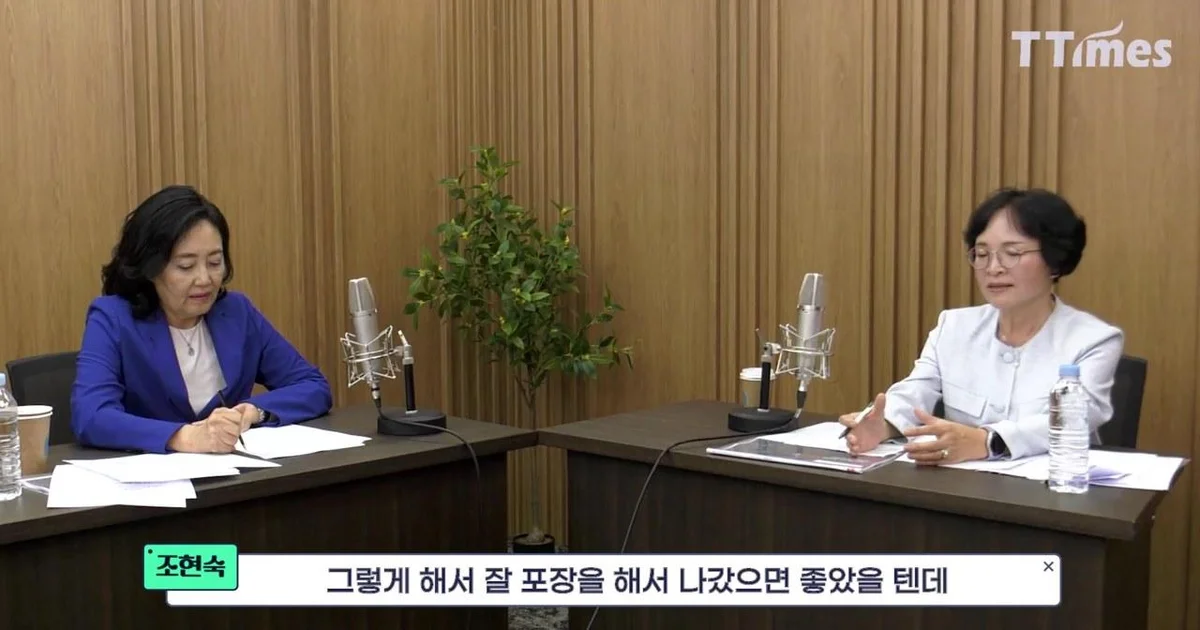
According to a T Times TV video, Cho Hyun-sook, Chairperson of the CODEGATE Security Forum, identified 'security internalization' as the core of security in the AI era during a recent interview. Chairperson Cho explained, "If you simply layer security onto a current system, it becomes a patchwork," adding, "If you keep attaching security systems to catch whatever malicious code appears, the system ends up being a patchwork." She continued, "If it is a new system, security must be internalized," emphasizing that "the Sovereign AI Foundation Model must also have security incorporated from the early stages of design."
Acceleration of AI Hacking and the Need for Agent Permission Control
AI technology is also completely changing the patterns of hacking. The video warned that the speed of hacking using AI can be overwhelmingly faster than that of human hackers. The video mentioned the danger of AI being used as a hacking tool, stating, "While it took an average of 2.2 years to penetrate vulnerabilities in 2018, using MitoSu takes only 20 hours."
In particular, the emergence of 'AI agents' that judge and act on their own is presenting new security challenges. As AI agents are granted various permissions such as sending emails, viewing documents, and making payments, the core issue has emerged as how far these permissions should be allowed. Chairperson Cho explained that it must be possible to control what the model has learned, whose data it has accessed, and the scope of its activities. She also suggested that humans must possess the ability to stop operations at any given moment while collaborating with AI.
Cyber-Physical Security and National Security Risks
The realm of security is also expanding beyond software into the physical world. Mentioning the importance of 'cyber-physical security,' Chairperson Cho warned that cyberattacks could lead to strikes on physical production facilities such as semiconductor factories or data centers. This is an issue directly linked to human safety in the era of 'Physical AI,' such as autonomous driving and smart factories.
Furthermore, the risk of 'cyber warfare,' where cyberattacks lead to the paralysis of national infrastructure, was also pointed out. It was noted that a single small piece of malicious code could spread through communication networks or power grids, neutralizing an entire nation. Chairperson Cho cited a rigid response culture and weak punishment regulations as security vulnerabilities in South Korea. She said, "When a problem occurs, it should be fixable immediately, but immediate response is difficult due to complex reporting systems," and "Strong punishment regulations to respond when an accident occurs must be established legally."
0Comments
Comments are currently disabled.