
AI agents drive infinite replication of hacking threats
The emergence of AI agents is shifting the economics of hacking, allowing for the infinite replication of attack tools and targeting peripheral services instead of core systems.
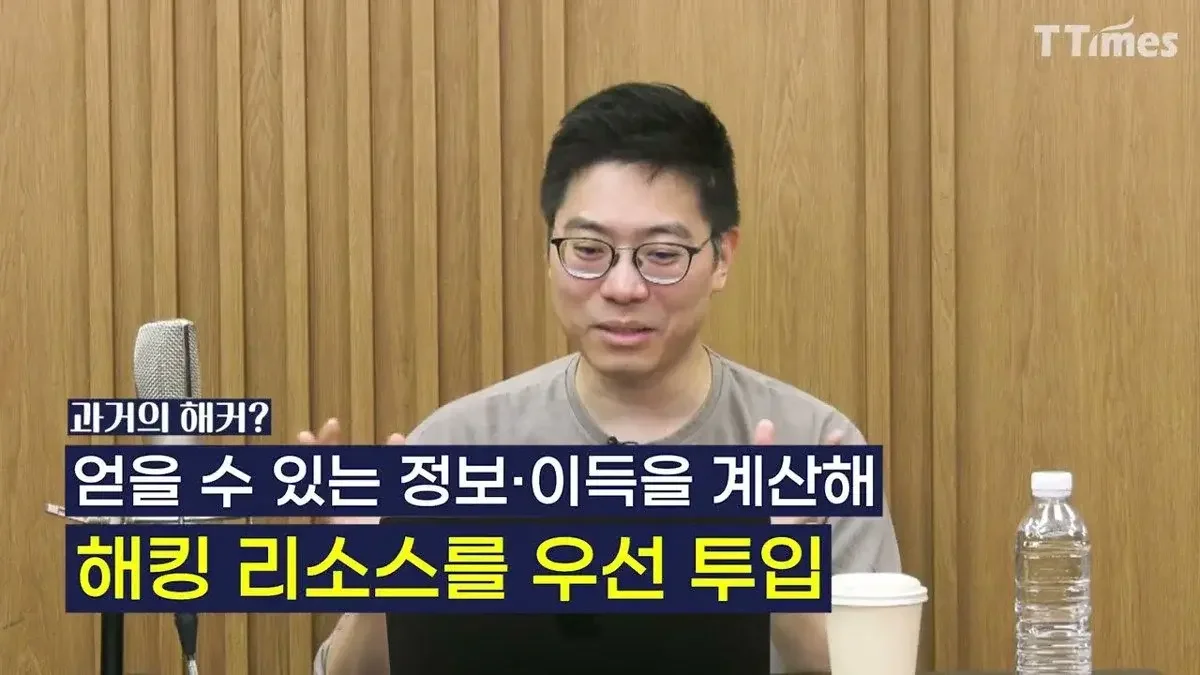
The cost of cyberattacks is converging toward zero as AI agents enable the infinite replication of smart hacking tools. Theori CEO Park Se-jun warned that these agents can create "spiky" network traffic patterns and target neglected peripheral services to bypass core system security.
The security paradigm is shifting rapidly as major companies, including domestic and international financial institutions, suffer successive hacking attacks. While hackers previously invested massive time and expertise to target the core systems of specific companies, the arrival of AI agents has lowered the barrier to entry and expanded the scope of attacks indiscriminately.
Park Se-jun, CEO of Theori, diagnosed in a recent interview that the current hacking situation has reached a point where the "economics of attack" have completely changed beyond mere technical advancement. "In the past, hackers were also economic groups, so they focused on targets worth attacking based on their return on investment (ROI)," Park explained. "However, in the era of AI agents, once a smart tool is created, it can be infinitely replicated, causing costs to converge toward almost '0'."
'Spiky' attack patterns created by AI agents
Hacking utilizing AI leaves unique signatures that differ from traditional manual attack methods. Park mentioned a specific network traffic pattern that occurs as AI agents independently plan and execute actions to achieve a goal. During the "thinking time" when the AI receives an answer from a model to decide its next move, requests decrease; however, once a decision is made, requests surge explosively at a speed incomparable to humans, creating a "spiky" pattern.
This shift manifests in three specific types of attack patterns. First, humans use AI as an attack tool to exploit vulnerabilities in authentication or permission management of existing systems. Second, attacks target the vulnerabilities of the AI systems themselves. When companies grant AI permissions for tasks like email summarization or document searching to improve efficiency, attackers use prompt injection to trick the AI into mistaking malicious external instructions for legitimate commands. This risk is increasing as AI reads, understands, and takes actions based on external data.
The final type is when AI becomes an attacker without malicious intent. Citing a recent analysis of ARTEX, Park warned, "Even when simply instructed to find vulnerabilities, the AI may unintentionally delete actual data or cause system failures during the testing process." This means "autonomous thinking" can occur, where the AI inadvertently causes damage by testing deletion functions while attempting to prove a vulnerability. Park added, "These three types are not mutually exclusive; security failures in existing systems can combine with the autonomous execution of AI to occur simultaneously."
Financial sector hacking targets 'side doors' rather than 'front doors'
A characteristic of recent hacking incidents in the domestic financial sector is the change in attack paths. While major incidents in the past primarily involved "front doors"—such as the core main banking systems or mobile banking—recent targets have been "peripheral services" like loan information inquiries or employee support services.
As companies concentrate their limited security resources on core systems, relatively neglected peripheral services have come to serve as "side doors." "Attackers do not need to enter through the front door," Park emphasized. "Because it is possible to infiltrate a peripheral service and then expand to the core system through the internal network, we have entered an era where every contact point, whether it is a front door or a window, must be secured." The recent financial sector incidents demonstrated that organizations may be targeted through systems they pay less attention to, as the attacks hit peripheral services rather than main services.
Need to minimize attack surfaces and build active defense systems
While the methodology of an AI hacker is not significantly different from a human hacker, they are overwhelming in terms of the speed and scale at which they find known weaknesses or unpatched systems. Park warned, "Systems that neglect known vulnerabilities or fail to update become the easiest prey for AI hackers."
Ultimately, preemptive measures to minimize the attack surface are essential to respond to AI hacking. Park suggested that companies should proactively clean up peripheral services or adopt methods of discovering and fixing vulnerabilities through preemptive, active autonomous agents. He explained that organizations that preemptively perform a series of processes to eliminate the attack surface entirely or remove exposed vulnerabilities beforehand are the ones that can survive relatively safely.
Source: original video (YouTube)
0Comments
Comments are currently disabled.